Cryptographic posture, from discovery to evidence
CONTINUUM is a Cryptographic Posture Management (CPM) platform that continuously inventories the cryptography on your hosts and across your network, then checks every asset against policies. When an asset breaks a rule, CONTINUUM opens a violation, uses your tags to set its severity, and tracks it from assignment to resolution.
Discovery
One inventory from the host and the wire
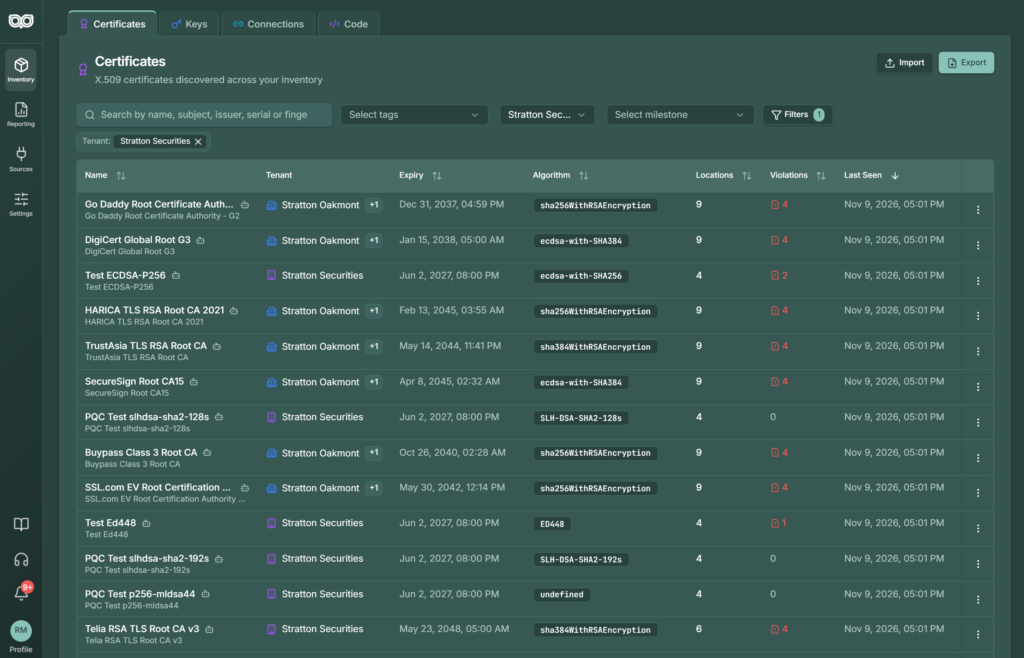
Each source sees cryptography from a different place. Certificates are deduplicated across the account, so the same certificate on fifty servers is one record linked to all fifty.
- CipherSight: certificates, SSH keys and encrypted volumes on Windows, Linux and macOS hosts.
- FlowSight: the TLS your systems negotiate, observed passively on the network.
- On request: AWS KMS keys and ACM certificates, and CycloneDX CBOMs you import.
Network
See what the wire actually negotiates
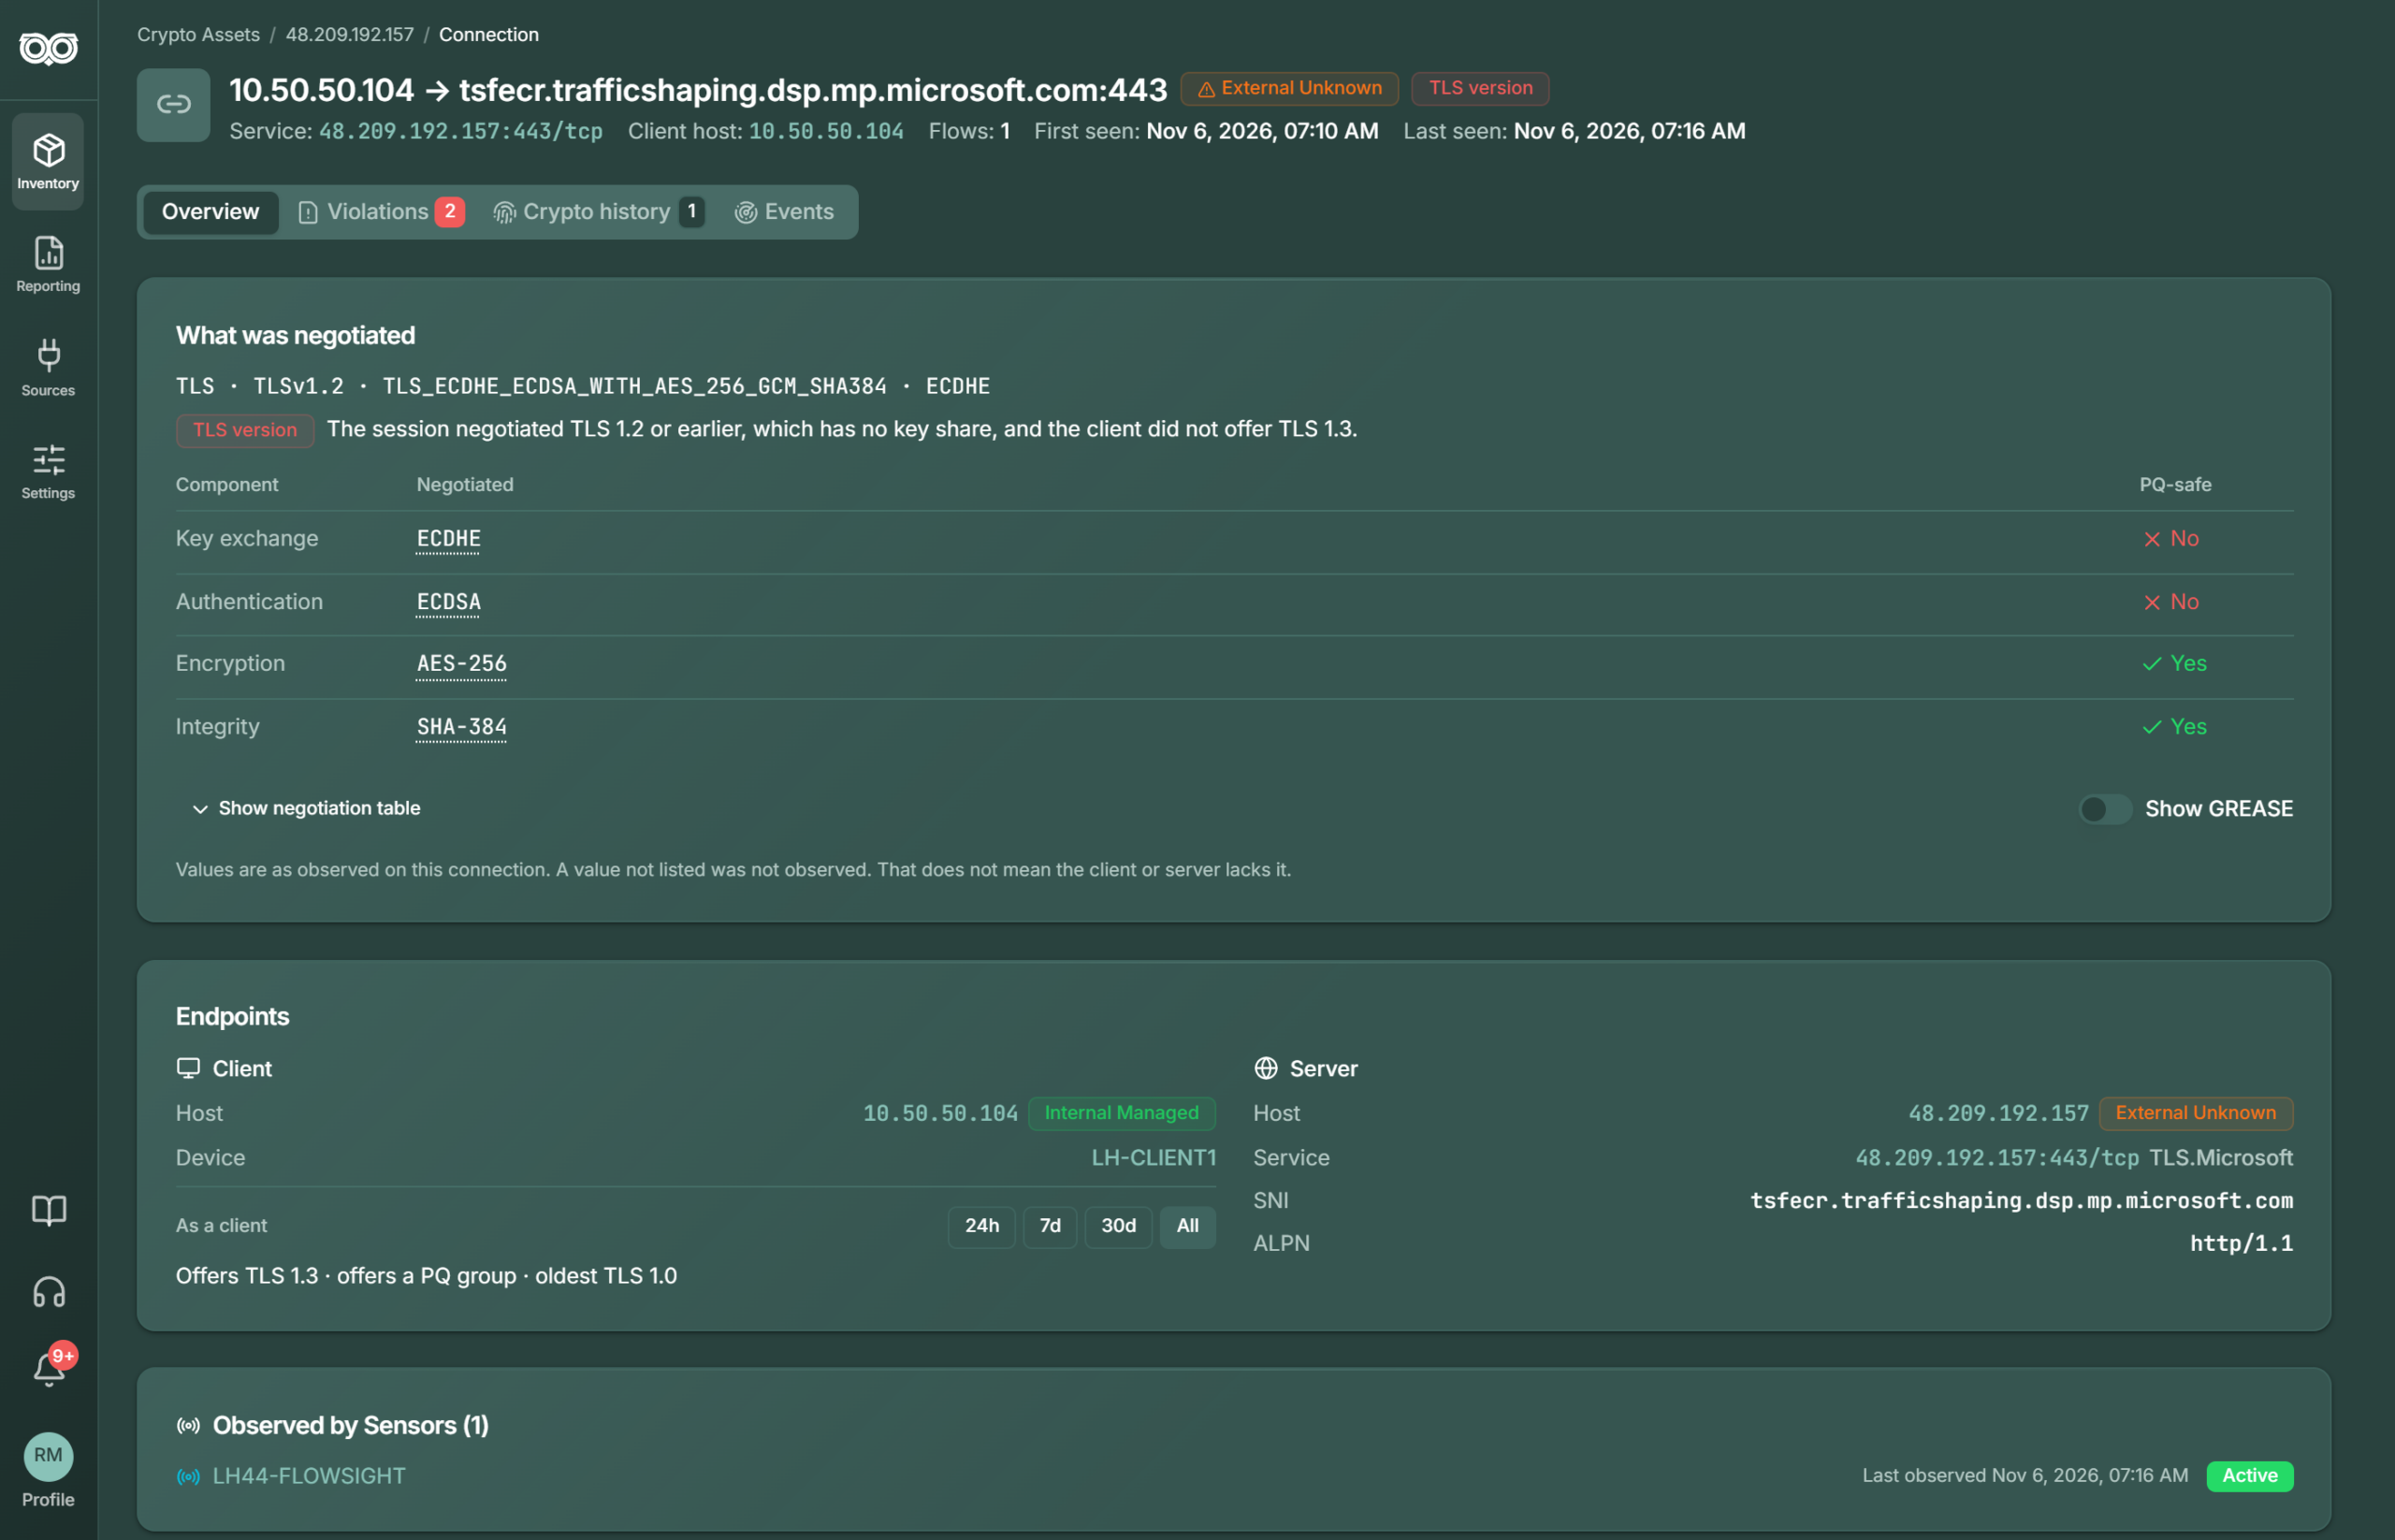
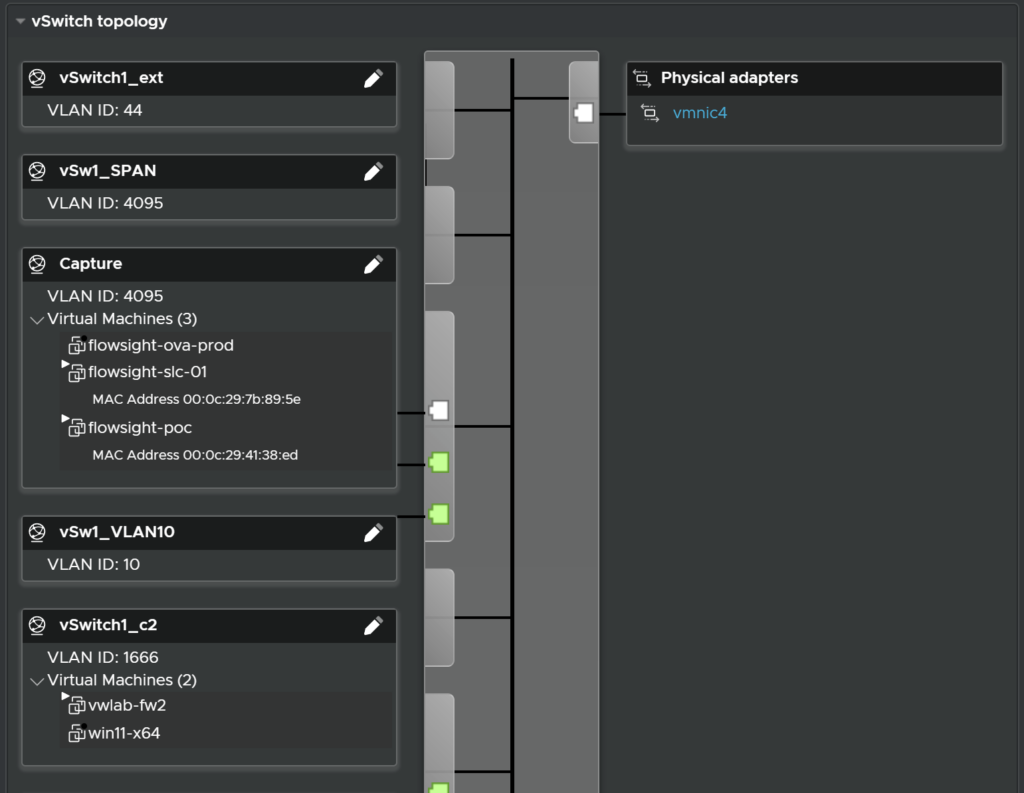
FlowSight reads a mirrored copy of traffic from a SPAN port, network tap or cloud traffic mirroring. It records TLS versions, cipher suites, key exchange, certificate exchange and client TLS capabilities, with no agent on the monitored host and no decryption. Devices no agent can be installed on enter the inventory this way. The engine underneath is nDPI, with more than 15 years of deep packet inspection behind it.
Endpoint
Add endpoint depth where you need it
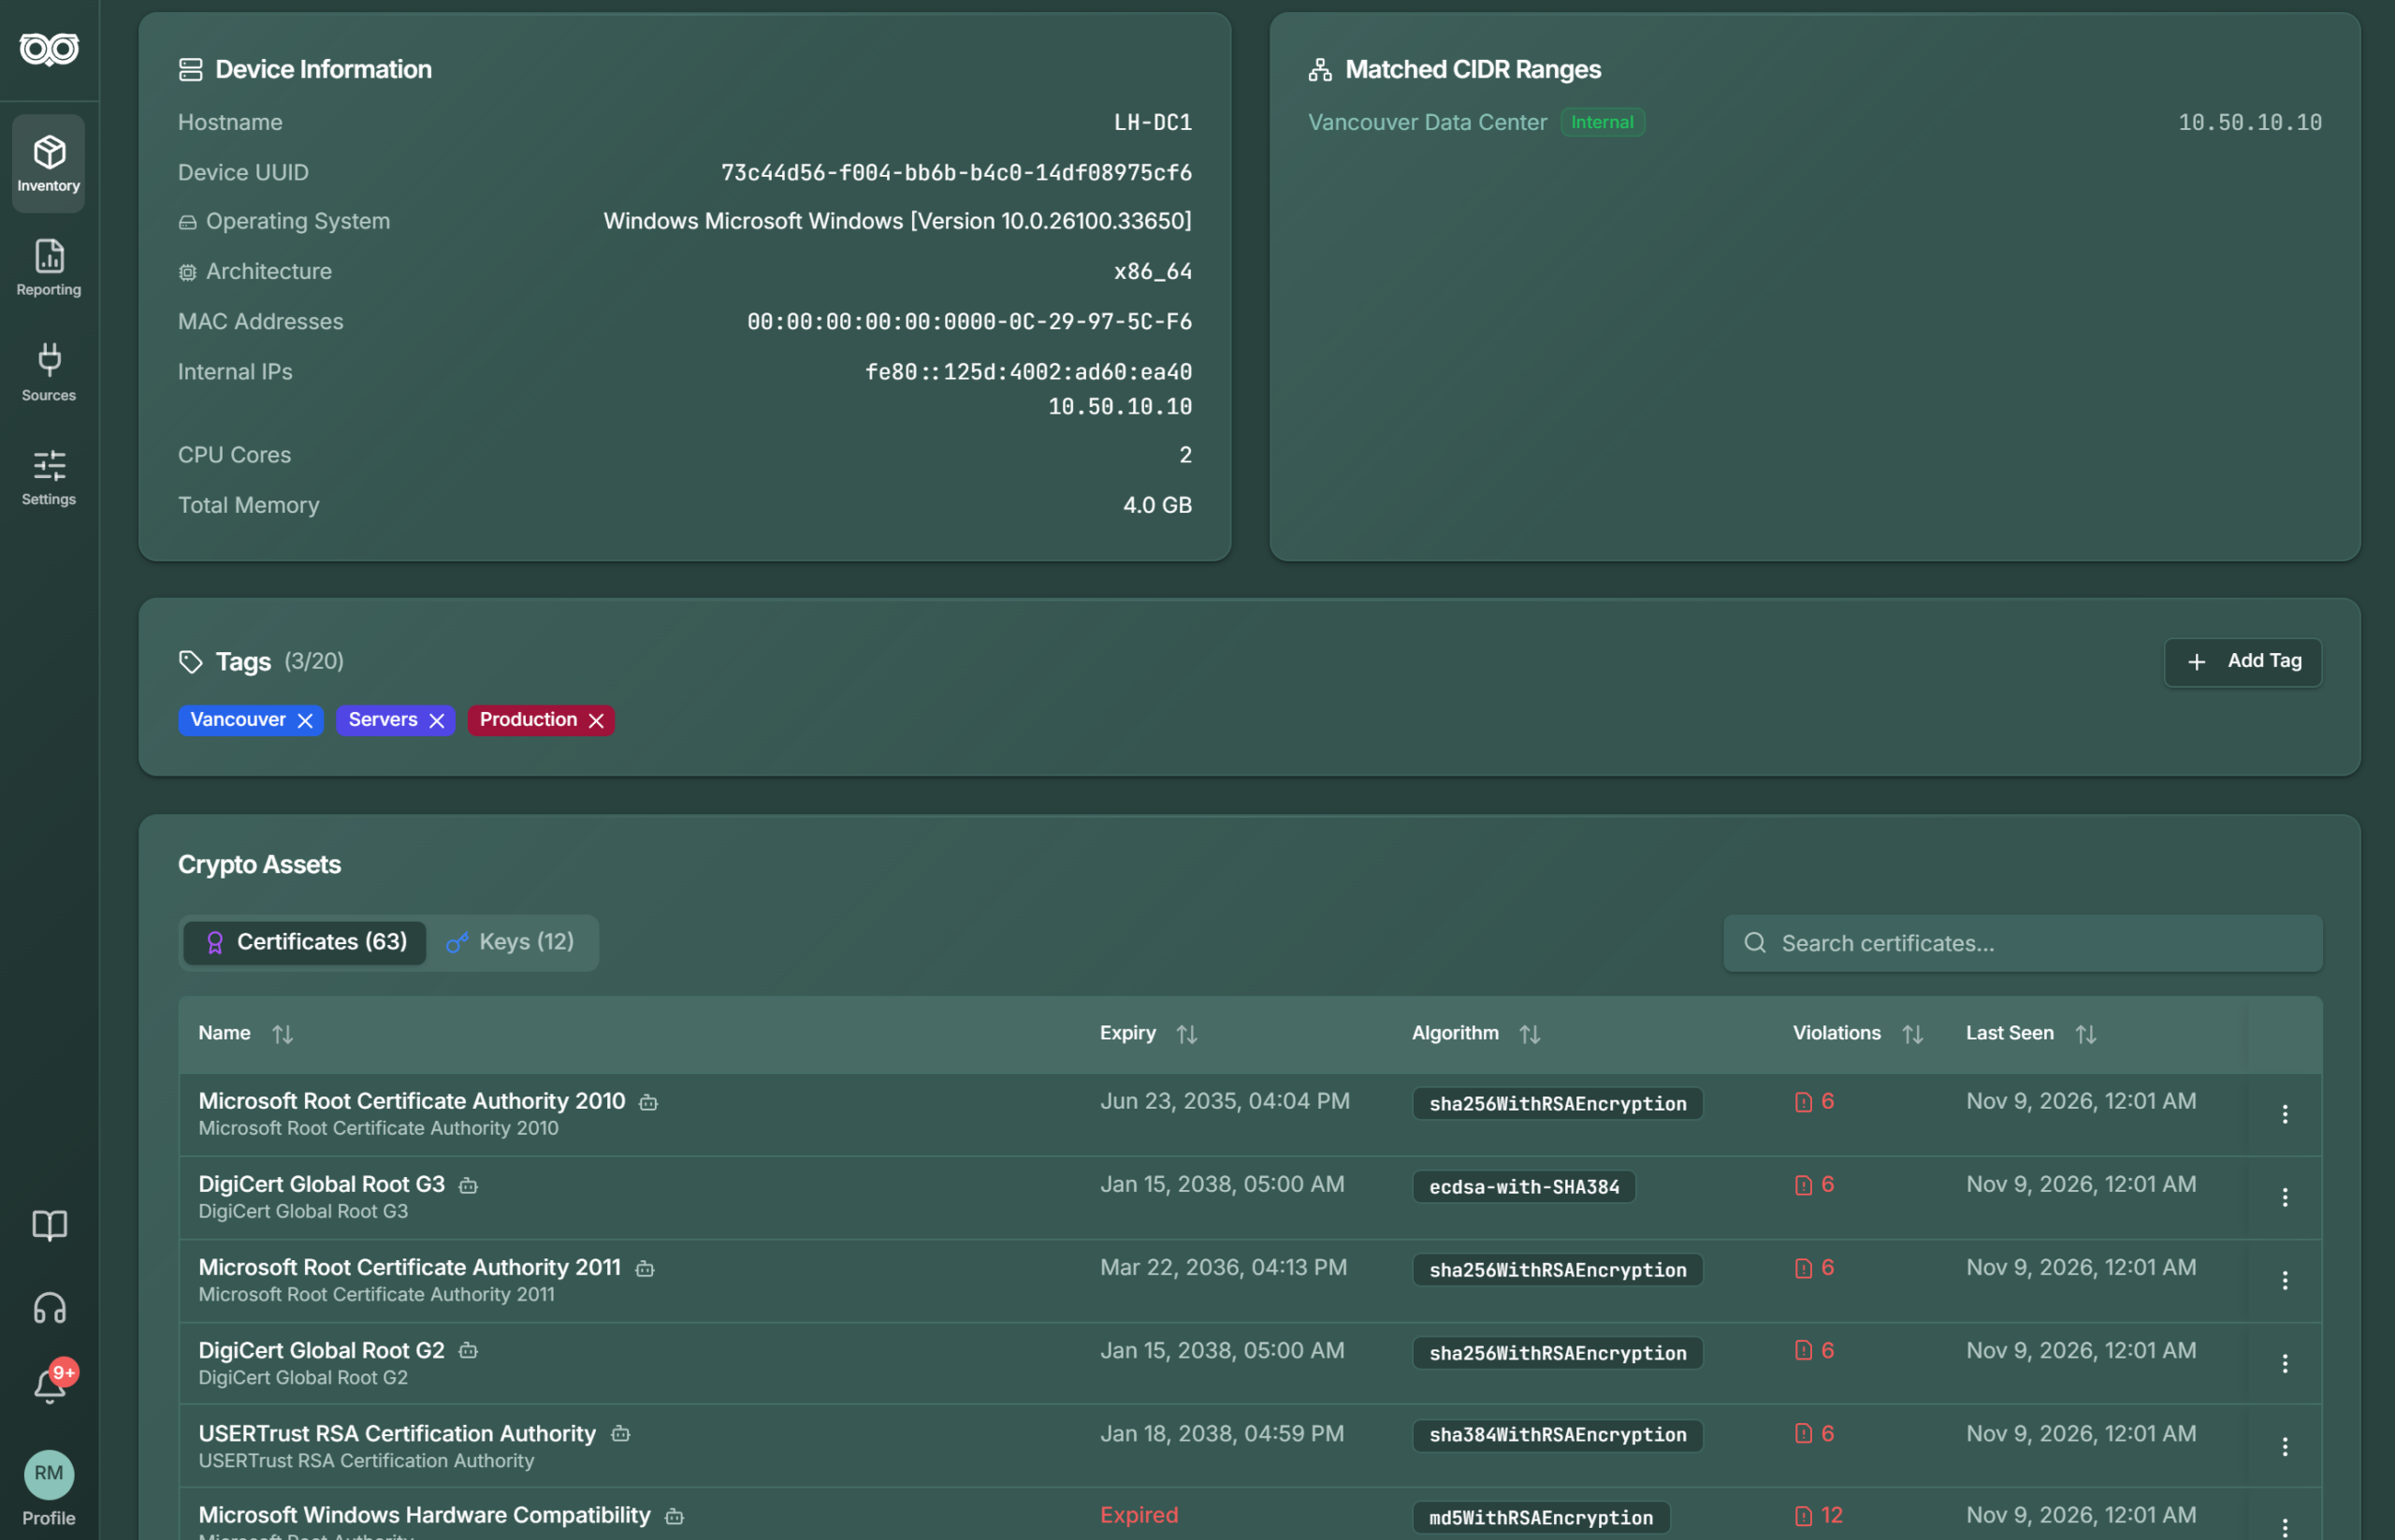
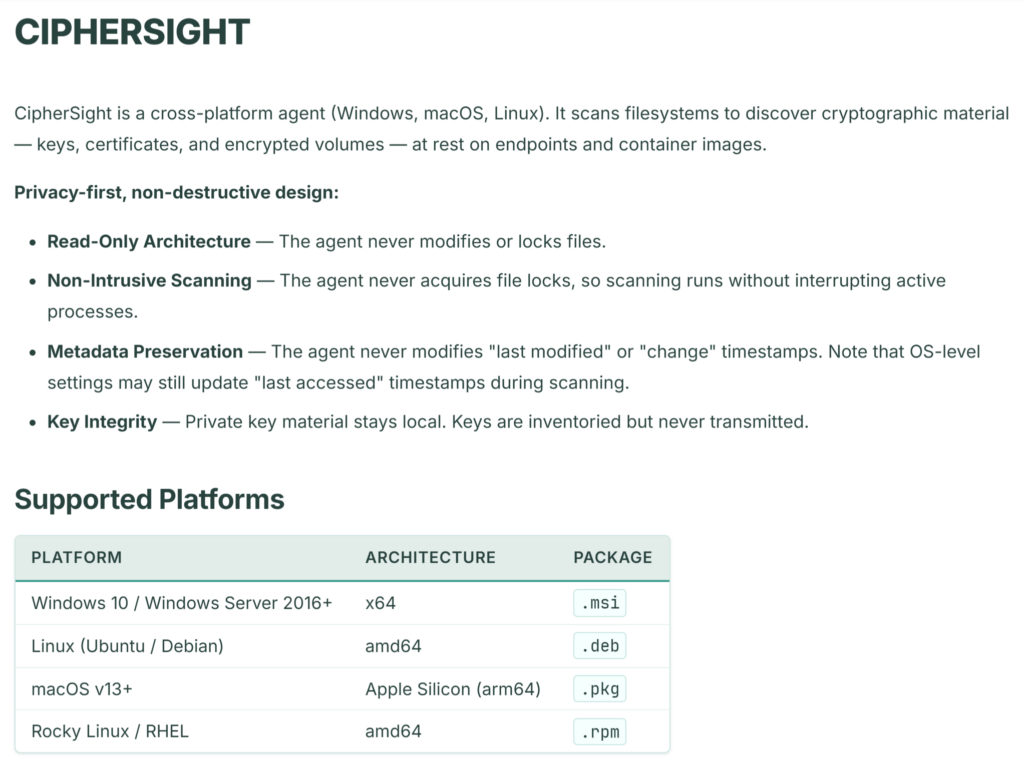
CipherSight finds X.509 certificates in PEM and DER files, Windows certificate stores and the macOS Keychain, along with SSH keys and BitLocker, LUKS and FileVault volumes. It runs on Windows 10 and Windows Server 2016 or later, Ubuntu, Debian, Rocky Linux, RHEL and macOS 13 or later on Apple Silicon. Only fingerprints and metadata leave the host.
Deployment
Start passive, then add depth
No application code changes and no inbound firewall rules. Every sensor connects outbound over HTTPS.
-
01 Register your sensors
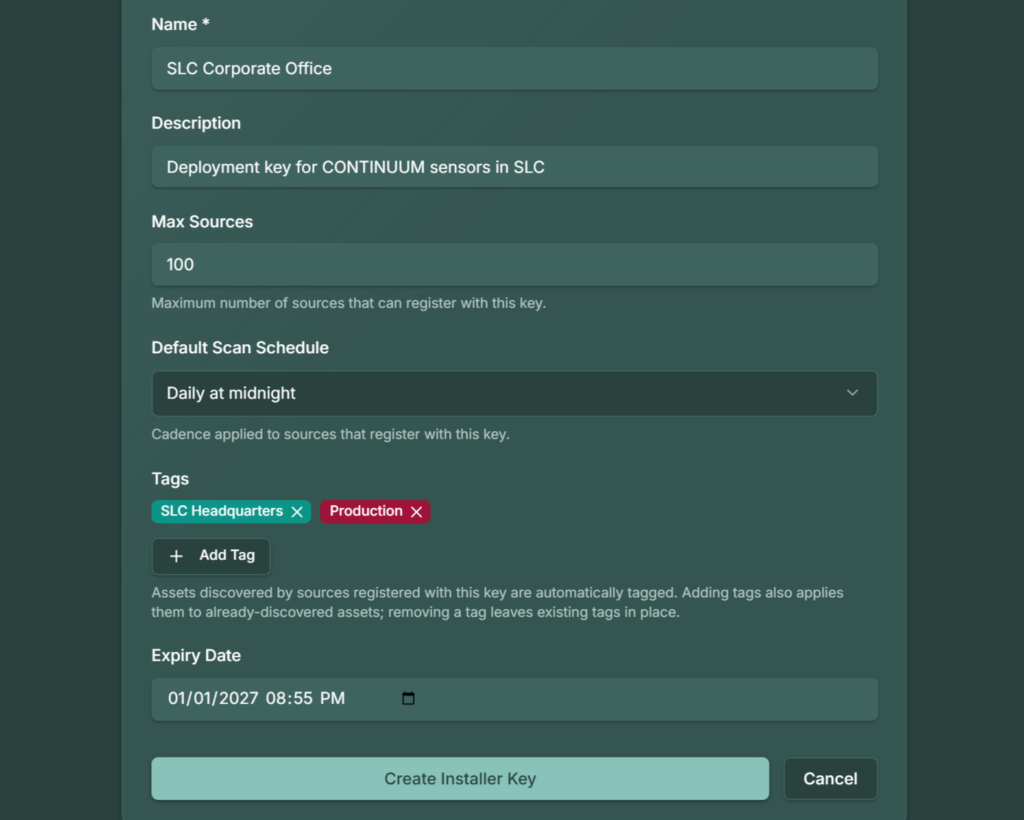
Each sensor registers with an installer key you generate and receives its own API key. Sensors trust only a certificate authority bundle built into the sensor, so a TLS-inspecting proxy needs a destination exclusion.
-
02 Watch the network
Point FlowSight at a SPAN port, a tap or cloud traffic mirroring. Findings from the TLS your systems negotiate arrive before any endpoint change is negotiated.
-
03 Add endpoint depth
Install CipherSight with the platform-native package on the hosts you choose. Certificates, SSH keys and encrypted volumes join the same inventory.
-
04 Activate policies and milestones
Turn on the default policies or your own, and group them under deadlines. Violations open automatically and the evidence reports fill in.
Policy
Policies that evaluate continuously
Twenty-three default policies cover six areas: asymmetric and key exchange, certificate health, symmetric encryption, hash functions, post-quantum standards and network handshakes. Policies start as drafts, you activate them per tenant, and active policies open a violation when an asset breaks a rule. Every change re-enters evaluation, so a renewed certificate with a weaker key opens a violation when the sensors next report it.
Rules built on published standards
Shipped rules evaluate against NIST SP 800-131A, SP 800-57 and SP 800-52, FIPS 186-5, FIPS 203, 204 and 205, and NSA CNSA 2.0. PCI DSS, SOC 2 and ISO 27001 are referenced.
Severity that follows your tags
Each policy sets a severity from Critical to Informational. Your tags can raise it for the assets that matter most, and the most restrictive setting wins.
Custom rules when you need them
Clone a default policy or write your own rules. Rules can test certificate detail such as subject and issuer, SANs and self-signed status.
Governance
Track every violation to a recorded outcome
Deadlines, exceptions and ownership all leave a record, so the plan you show an auditor is the one the platform enforces.
Milestones
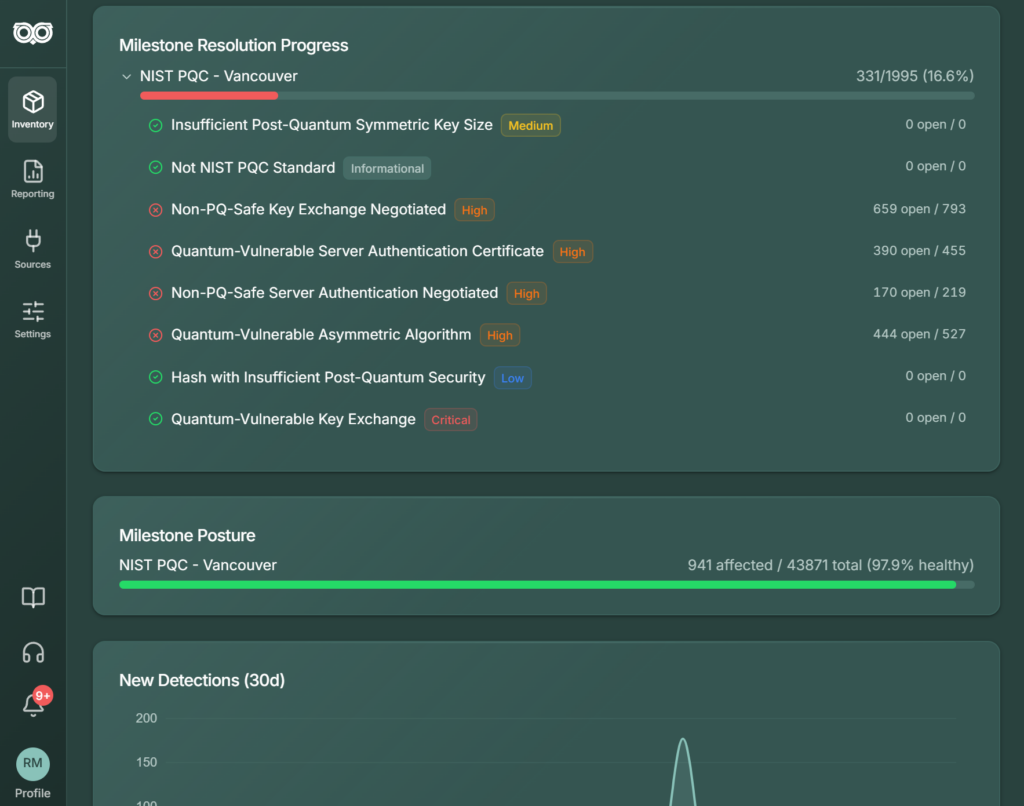
Group policies under a deadline, scoped by network range or tag. Four ship by default: Best Practices, NIST, PQC and PQC Optimized. Each reports completion and the share of in-scope assets with no open high or critical violation.
Exclusions
Exclude an asset permanently or until a date, scoped to a tenant, enterprise or account, with a recorded justification. When a time-bound exclusion lapses, its violations reopen.
Violation lifecycle
Violations move from Open through Acknowledged and In Remediation to Accepted, Transferred, Resolved, Retired or Excluded. Assignment, watchers and notes travel with them, and closing one requires a written reason.
ServiceNow hand-off
With the integration enabled, violations become ServiceNow incidents and their status syncs back. Available on request.
Built for an audit trail
5
severity levels, from Critical to Informational
8
violation states, each change logged
23
default policies across six areas
Evidence
Evidence you can export on demand
CycloneDX CBOM
Export the cryptographic bill of materials in CycloneDX 1.6 or 1.7, plus CSV exports of certificates, keys and negotiated protocols.
Posture PDF
Overview KPIs, asset health, top risks, protocol health and post-quantum readiness, including the PQ readiness percentage and its comparison with 30 days earlier.
Compliance PDF
Burn-down for each milestone, days to deadline and on-track or at-risk status. Audit logs record platform activity.
Evidence toward OMB M-26-15’s automated inventory and central CBOM, PCI DSS v4.0.1 Req. 4.2.1.1 and 12.3.3, and CNSA 2.0 milestones. CONTINUUM produces the evidence; it doesn’t make you compliant.
Integrations
Feeds the systems you already run
A read-only Developer API with six scoped read permissions lets your CMDB, GRC tool or data pipeline pull certificates incrementally, using changed-since filters, and violations on demand. Single sign-on works over SAML 2.0 or OpenID Connect, and the CBOM exports in CycloneDX 1.6 or 1.7.
Enabled on request: AWS KMS and ACM inventory · ServiceNow Incident Management · CycloneDX CBOM import
Questions from the technical review
The answers below come up in most security reviews. For anything else, ask us.
How do sensors connect to the platform?
Outbound over HTTPS; the platform never initiates a connection into your network. Each sensor registers with an installer key you generate and receives its own API key.
Does FlowSight decrypt traffic?
No. It reads handshake metadata from a mirrored copy of traffic and doesn’t need to decrypt anything.
How is our data separated from other customers?
Data is strictly isolated between accounts. Within your account, users see only the tenants they’re granted, and policies and exclusions inherit downward.
Is QubitOwl SOC 2 certified?
QubitOwl’s SOC 2 audit is in progress. There is no completed attestation today, and we do not claim one. The platform is architected to SOC 2 Type II requirements, and we will share the report when the audit completes.
Can we run CONTINUUM in our own environment?
The default is our multi-tenant SaaS. CONTINUUM can also run in your own AWS environment, where you hold operational and security control of the platform; that is delivered as a scoped engagement with our engineers.
Does CONTINUUM score risk?
It doesn’t assign a per-asset risk score. It reports the PQ readiness percentage, milestone completion and per-milestone posture.
What does PulseSight cover today?
PulseSight reads IBM z/OS connection telemetry off-host, with no QubitOwl software on the LPAR, and shows it in the console. It is in Limited Availability, and its events are not yet part of the inventory or CBOM.
How is CONTINUUM licensed?
Licensing counts Active Machine Identities (AMIs): persistent machines the platform has observed in the trailing 90 days, whether servers, VMs, cloud instances, network devices, endpoints, or connected medical devices. A machine counts the same way whether a sensor saw it or a connected integration reported it active, and a machine seen through several sources counts once. We count machines, never certificates or findings — a deeper scan never raises the bill.
What does the evaluation produce, and what doesn’t it?
The platform produces a CBOM, the quantum-vulnerable algorithms in use, the PQ readiness percentage and the Posture and Compliance PDFs. Framework mapping and a migration roadmap come from the engagement team, not the product.
Can a consulting practice run several clients?
Yes. Account, enterprise and organization scoping lets a practice run each client in its own tenant, with role-based access.
Start with a four-week proof of value
Four weeks on a representative part of your environment, in a dedicated tenant, for roughly four hours of your team’s time.
CipherSight reads private keys on the host and never transmits them. Only fingerprints and metadata leave.